Jan 24, 2026 · AWS
Automating Contact Updates Across Accounts In Your Organization
How to set primary and alternate AWS account contacts across an Organization with the account API, from the management account.
Read More →For MSPs & AWS consultants
AWS Hosted Client → Org → Account inventory plus temporary role assumption and console access with External ID.
Deploy a role or reuse one, without setting up Identity Center in every client Organization.
So you can see the whole book of client Orgs and jump into the account you need.
External ID is how AWS checks the assume-role request came from Quiverstone.
No payment information required
Temporary STS credentials only. Your browser session, their CloudTrail. We never store long-term client credentials. How access works
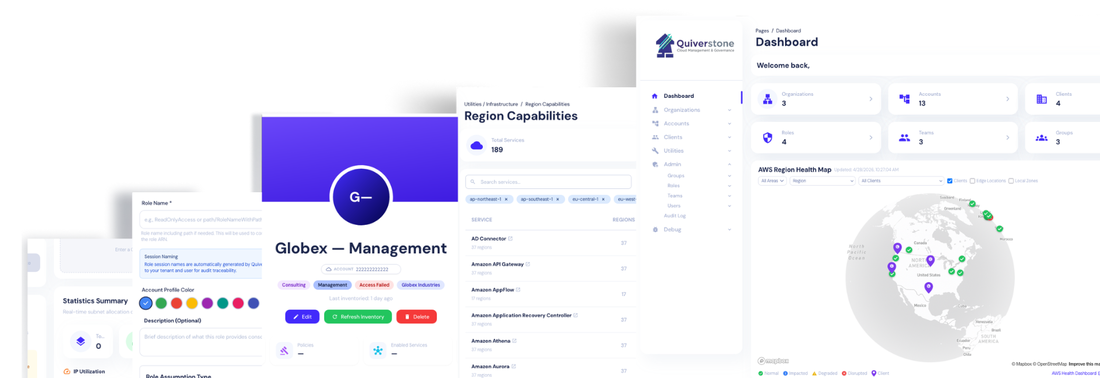
Everything in one place

Portfolio of unrelated client Orgs in one place — not one customer’s landing zone.

Member accounts discovered automatically when you enroll an Org; standalones sit beside them.

Search and discover details for resources across accounts or customer organizations.

Assume-role with External ID (direct or chained). Your browser session, their CloudTrail.
as of Jan 2026
100+
Organizations managed
1K+
AWS accounts governed
10+
Years in AWS management

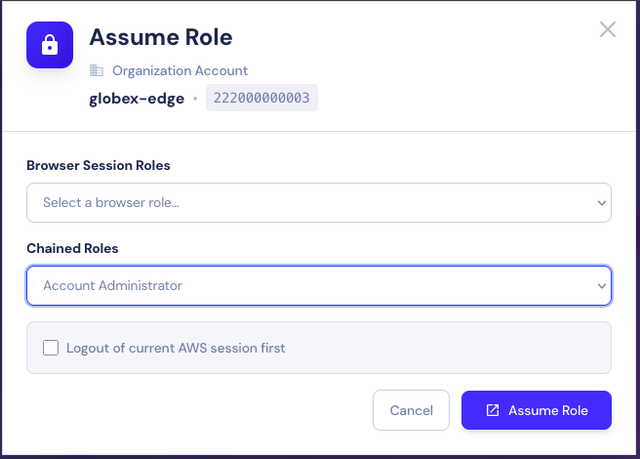
Deploy a role. Connect your clients.
Temporary STS credentials only. Your browser session, their CloudTrail. We never store long-term client credentials. How access works
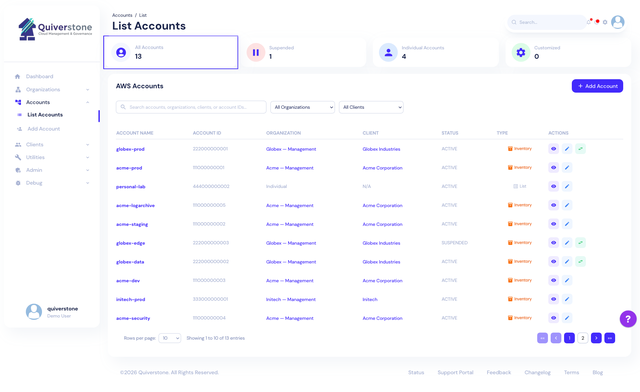
Client → Org → Account inventory
Bring enrolled AWS Organizations and standalone accounts into one inventory, so you can answer “what accounts does this customer even have?” Quiverstone discovers member accounts when you connect an Organization.
Plan limits apply to the Organizations and standalone accounts you enroll. Member accounts inside an enrolled Organization are unlimited.

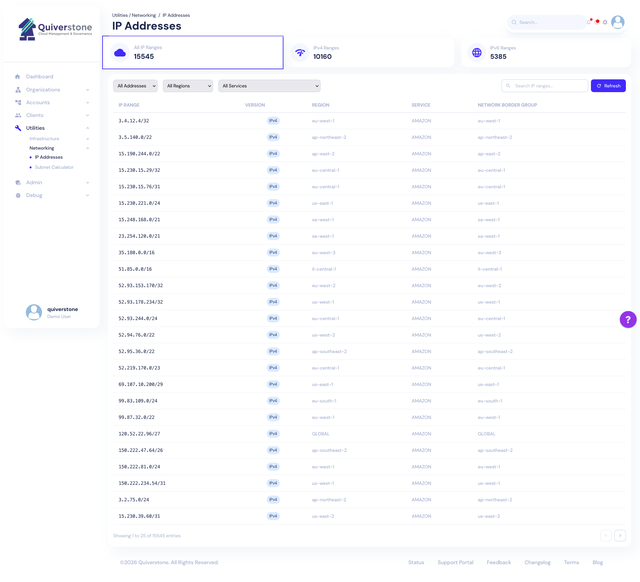
Tools for day-to-day client work
Keep common tools, references, and deployment templates alongside your client work. Teams can share their own libraries so operators can follow a consistent process.
Start with inventory and access across your client environments, then use the utilities that fit the work in front of you.
Stop hopping Identity Center portals, vaults, and spreadsheets. Discover Orgs and accounts once; assume a role in one click.
Fewer unbillable hours on access archaeology. Free to prove it; Consultant and Pro are priced for practice scale.
One inventory of how you actually reach each client estate — knowledge in the cockpit, not on a laptop.
Practice economics: Customer, Org, Project, and engagement type (Resale, Managed Services, Professional Services) keep retainers and scoped work billable.
Founder / Principal
10+ years of AWS management and governance, including DOD/DOI work and GovCloud/FedRAMP environments.
LinkedInQuiverstone does not store long-term client credentials. Access is temporary STS role assumption with External ID, using your browser session, and the session is recorded in that account’s CloudTrail. This is the same process enterprise tools use: an IAM role with a trust policy and External ID.
Deploy a Quiverstone-managed role through CloudFormation or StackSets, or reuse an existing role that already has the required trust. You choose Read-Only, Power User, Administrator, or a custom policy. Team access is scoped by Group × Account × Role.
No. Member accounts inside an enrolled Organization are unlimited on every tier. Plan limits apply to the Organizations and standalone accounts you enroll, plus clients and seats.
Consultant and Pro include a 5-day trial so you can use that tier before you are charged. No credit card is required to begin. Free is $0 with no expiration.
From the blog
Jan 24, 2026 · AWS
How to set primary and alternate AWS account contacts across an Organization with the account API, from the management account.
Read More →
Jan 10, 2026 · AWS
The AWS Distributed Load Testing solution runs JMeter, Locust, or K6 on Fargate. One test pushed CloudFront past 50 TB in five minutes.
Read More →
Jan 2, 2026 · Platform
Quiverstone is inventory and External-ID assume-role for MSPs who manage many unrelated client AWS Organizations in one place.
Read More →For MSPs and AWS consultants managing a portfolio of client AWS Organizations.